CTF Prep
Linux Basics Warmup
Start with shell navigation, permissions checks, and note-taking in a guided environment.
CTF Prep
Web Recon Starter
Practice identifying services and investigating HTTP responses using command-line recon techniques.
CTF Prep
Log Hunt
Analyze suspicious activity from logs and extract the highest-risk indicators quickly.
CTF Prep
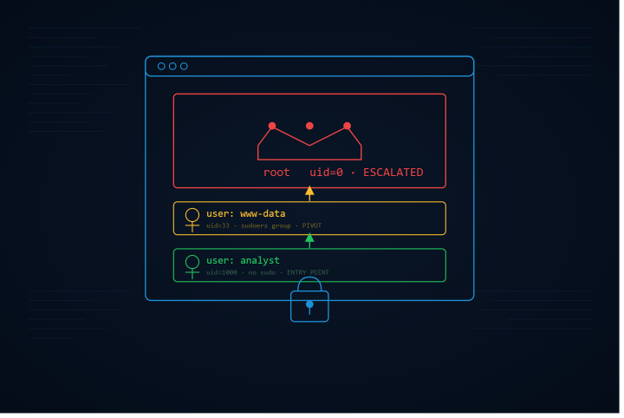
Privilege Escalation Trace
Correlate authentication and sudo activity to identify the first escalation path and impacted account.
CTF Prep
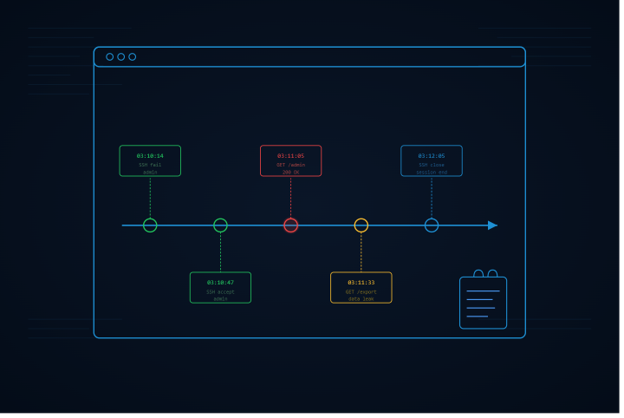
Incident Timeline Reconstruction
Rebuild chronological incident flow from mixed security events and produce ordered timeline evidence.
CTF Prep
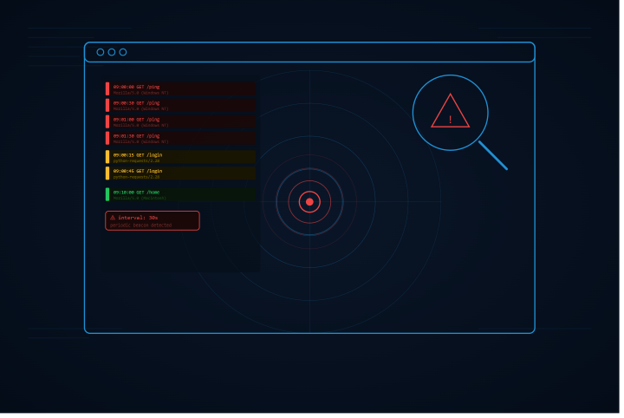
Log Hunt: Suspicious Beaconing
Detect periodic callback patterns in HTTP access logs by analysing user-agent strings and request intervals.
CTF Prep
Phishing Header Analysis
Inspect synthetic email headers to detect display-name lures, Return-Path mismatches, and SPF/DKIM failures that reveal sender spoofing.
CTF Prep
IAM Least Privilege
Repair a synthetic over-permissive cloud IAM policy to the minimum permissions a fictional backup job actually needs — no wildcards, no extra actions.